AI governance training in SingaporeA rule people will actually follow.
AI governance training for Singapore organisations whose staff are already using tools the policy has not approved.
- Two tiers
- Whole of org or leadership
- In person or remote
- Tailored to your policies
- Singapore, in person or hybrid
Singapore
For Singapore organisations that already have shadow AI
Someone has already put a draft into a tool nobody approved. The policy has to be something a banker, an operator or an adviser will follow on Monday, not a file that sits unread.
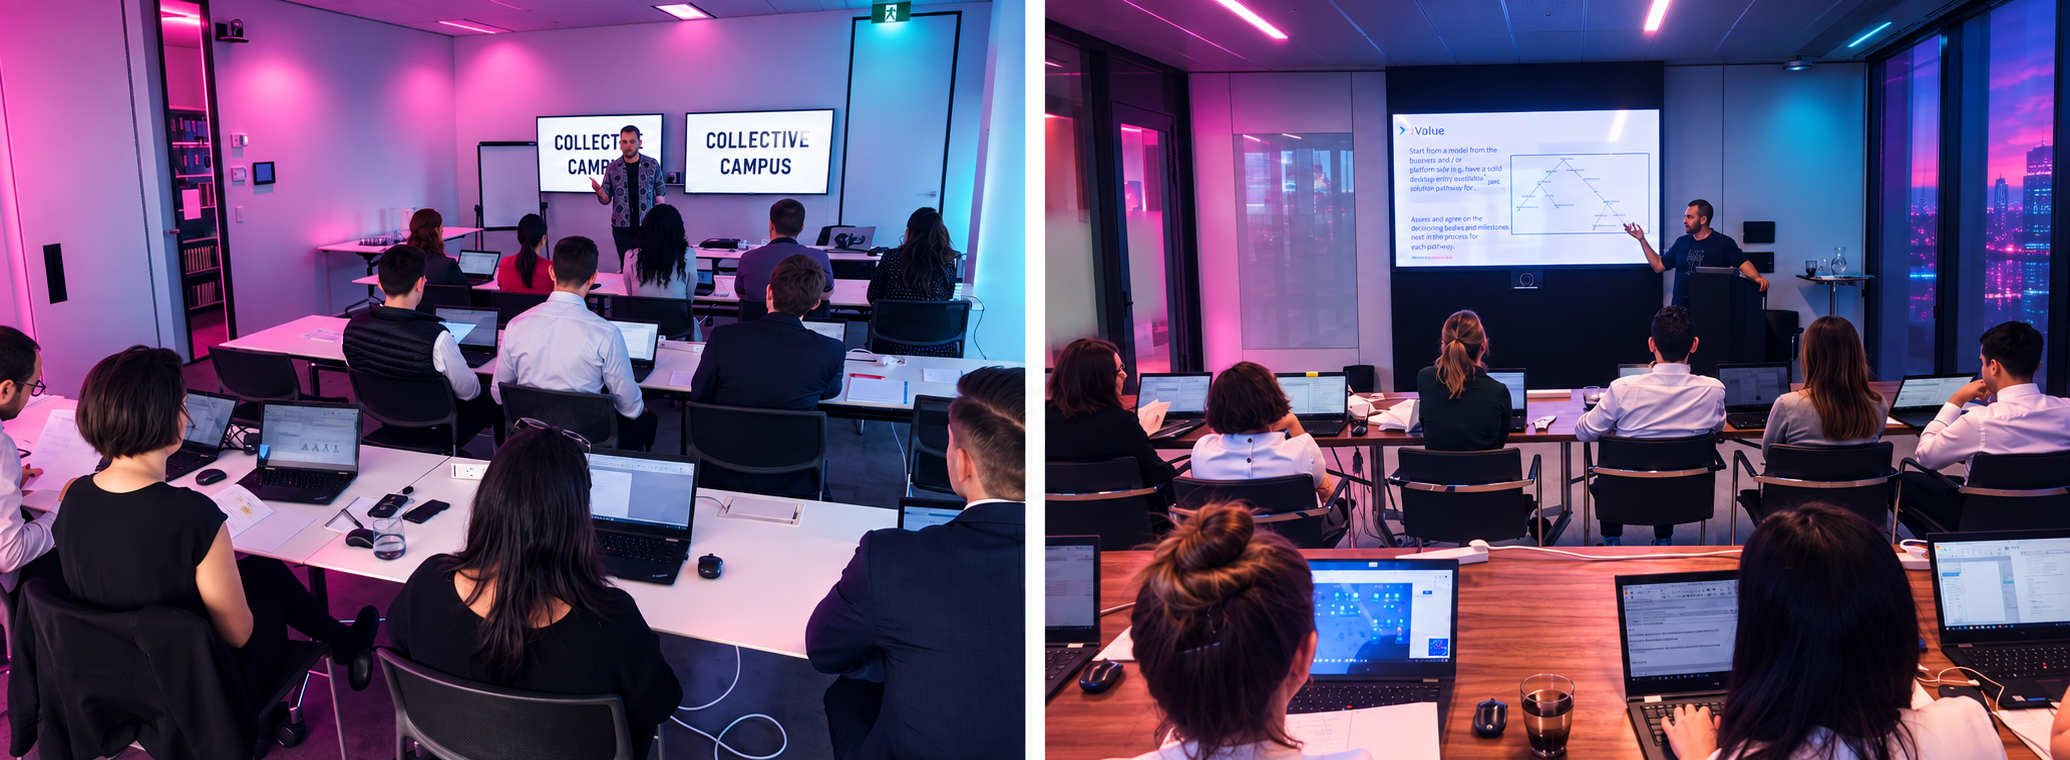
We run two tiers from Singapore: a half day for staff, and a day for leaders who classify risk, name owners and approve use cases. Cohorts can sit in the city or join on Singapore time. We map NIST, ISO 42001 and the EU AI Act onto your own rules.
- Staff foundations and a leadership day, in Singapore or on Singapore time.
- Shaped around your acceptable-use rules and the data that must stay inside.
- Plain language for staff. An operating model for the people who approve tools.
- Either tier can run alone. Large organisations usually need both.
◆ Trusted by teams at ◆



The problem
Rolling out AI is easy. Governing it is not.
Shadow AI everywhere
Staff pasting sensitive and client data into tools no one approved or vetted.
One bad output
A single hallucination or biased decision becomes a legal, regulatory or reputational problem.
The rules are moving
EU AI Act, privacy law, sector regulators. "We didn't know" is no longer a defence.
Governance kills adoption
Heavy-handed rules freeze the very innovation you rolled AI out to get.
Built on the standards
Grounded in the frameworks that matter
NIST AI RMF
The risk operating model: Govern, Map, Measure, Manage.
ISO/IEC 42001
The certifiable AI management system standard.
EU AI Act
Risk-tiered legal obligations, enforceable from 2026.
OECD and local guardrails
Responsible AI principles, plus the rules in your jurisdictions.
Two tiers
Two programs. Most large organisations need both.
AI Foundations for Everyone
All staff. Literacy and responsible use for the whole organisation. Every employee gets the guardrails to use AI safely and confidently: what is okay, what is not, and how to spot when AI gets it wrong. Half day. Scales across the company. In person or remote.
AI Governance for Leaders
Leadership. The operating model for executives and governance owners. Classify risk, assign ownership, approve use cases and stand up a model mapped to NIST, ISO 42001 and the EU AI Act. One day. In person or remote.
The curriculum
Foundations
Leaders get the operating model. All staff get everyday use. Shared modules run in both rooms.
BOTH
Why AI governance matters
The risk and reward case, and what goes wrong without guardrails.
BOTH
The regulatory landscape
EU AI Act, NIST, ISO 42001 and local rules, in plain English.
LEADERS
Risk classification
Tiering AI use cases from minimal to high risk.
Responsible AI principles
What good use looks like
BOTH
Fairness and bias
Where bias enters, and how to spot and mitigate it.
BOTH
Transparency and disclosure
Explaining AI decisions, and telling people AI is in use.
BOTH
Accountability and oversight
Human in the loop, and who owns an AI decision.
BOTH
Privacy and data governance
What data can go into AI: personal information, consent, residency.
Everyday governance
What staff do on a Tuesday
ALL STAFF
Acceptable use and shadow AI
Approved versus unapproved tools, and reining in shadow use.
ALL STAFF
Data security and confidentiality
Not leaking sensitive data. Prompt hygiene. Intellectual property.
ALL STAFF
Output risk and over-reliance
Hallucinations, verification, and when not to trust it.
BOTH
IP, copyright and ownership
Who owns outputs, and what training data and inputs expose.
Operating model
What leaders put in place
LEADERS
Roles and accountability
An AI governance council, a RACI, and clear ownership.
LEADERS
Use-case intake and approval
A lightweight process to vet AI before it goes live.
LEADERS
Monitoring and incident response
Logging, monitoring, and what to do when AI misfires.
LEADERS
Vendor and third-party risk
Vetting AI vendors and how they handle your data.
People and culture
Guardrails that still let people move
ALL STAFF
AI literacy for all staff
A baseline so everyone uses AI responsibly.
BOTH
A responsible AI culture
Safe to raise concerns and report issues early.
BOTH
Governance without killing innovation
Guardrails that enable adoption, not freeze it.
What you'll get
What changes
- Staff who use AI safely, without leaking data or blindly trusting output
- A shared, plain-English acceptable-use standard everyone actually understands
- Leaders equipped to classify risk, assign ownership and approve use cases
- A governance operating model mapped to NIST, ISO 42001 and the EU AI Act
- Guardrails that enable AI adoption instead of freezing it
Format and logistics
How it runs
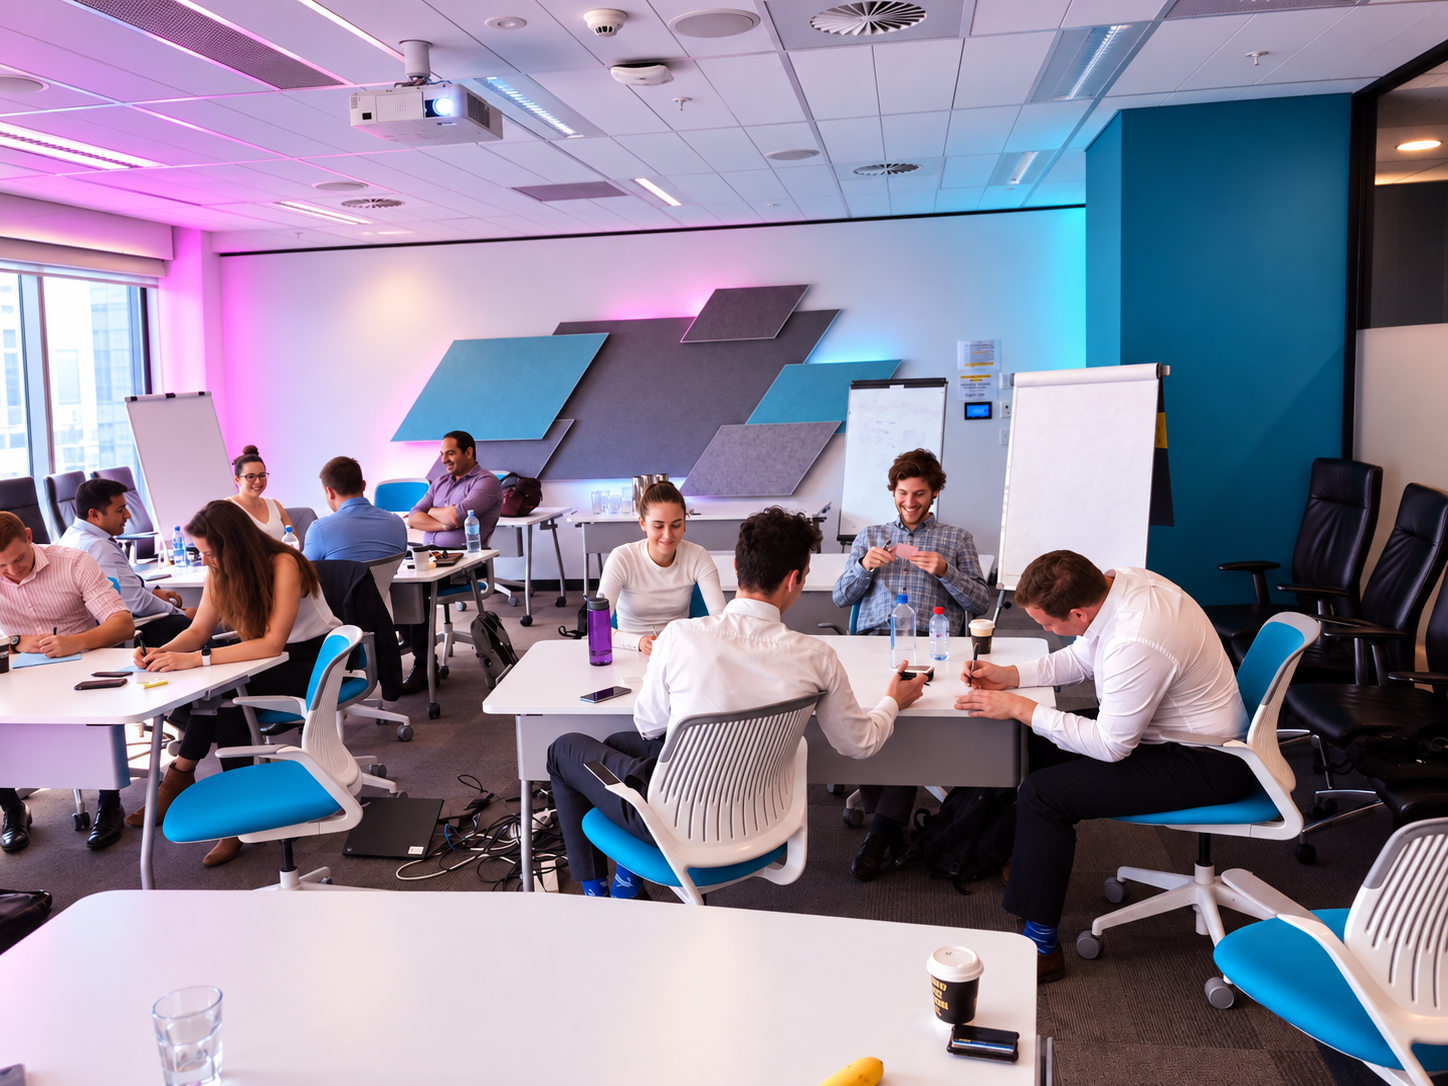
All-staff tier
Half day, and it scales across the company via multiple cohorts.
Leadership tier
One day for executives and the governance team.
Delivery
In person or purpose-built remote.
Tailoring
Built around your policies, tools, jurisdictions and risk appetite.
Facilitator
Steve Glaveski
Founder of Collective Campus, 2× Wiley author and HBR contributor on AI and the future of work. Steve has helped 100+ organisations adopt AI and innovation responsibly, and he runs these programs himself.
Proof
Grounded in NIST, ISO 42001 and the EU AI Act
These are the frameworks regulators, auditors and customers use when they ask whether AI is under control. Leaders leave with an operating model mapped to all three. Everyone else leaves with a plain-English standard for what is okay on a Tuesday.
NIST AI RMF
Govern, Map, Measure, Manage. The risk operating model leaders leave able to use.
ISO/IEC 42001
The certifiable management system for AI, translated into roles and routines.
EU AI Act
Risk-tiered obligations, enforceable from 2026, mapped to what your people actually do.
Singapore
Questions about running this in Singapore
Can we run the leadership day separately in Singapore?
Yes. Risk owners and the people who approve use cases belong in that day. Staff cohorts can run in Singapore or on Singapore time.
Will you lecture through the statutes?
No. We map NIST, ISO/IEC 42001 and the EU AI Act onto the rules you already have, then turn that into what a person does on Monday.
How do we book Singapore governance training?
Use the contact form. Tell us which tools staff use, what data is sensitive and whether you need the staff tier, the leadership day or both.
Will this stop people using AI?
Ungoverned use is already happening. The aim is an approved path that is faster than the shadow tool.
Related programs
Where this sits with the other AI work
Adopt AI with confidence, top to bottom.
Tell us where you are in your AI rollout and we will shape the right mix of both tiers.